

Hospitals Face Increased Risk of Data Breaches
|
By HospiMedica International staff writers Posted on 26 Apr 2017 |


|
A new study suggests that as health providers adopt health information technology, they increasingly suffer from data breaches.
Researchers at Michigan State University, Ball State University, and Johns Hopkins University conducted a retrospective data analysis of data breaches reported to the U.S. Department of Health and Human Services between October 2009 and December 2016. By law, U.S. hospitals covered by the Health Insurance Portability and Accountability Act (HIPPA), must notify the HHS of any breach affecting 500 or more individuals within 60 days of the discovery of the breach.
The results revealed that during the study period, healthcare providers reported 1,225 of the 1,798 recorded breaches, while business associates, health plans, and healthcare clearinghouses reported the remaining 573 data breaches. Of these, 257 breaches were reported by 216 hospitals; importantly, 33 hospitals experienced more than one breach, many of them large, major teaching hospitals, such as UC Davis Medical Center (CA, USA) and Henry Ford Hospital (Detroit, MI, USA). The study was published on April 3, 2017, in JAMA Internal Medicine.
“This research reinforces the critical trade-off patient’s face: healthcare systems having access to information they need, versus a hacker planning to spend your savings at Best Buy,” said lead author Xuefeng Jiang, PhD, of MSU, and colleagues. “While the law requires health care professionals and systems to cross-share patient data, the more people who can access data, the less secure it is.”
A data breach is defined as a security incident in which sensitive, protected, or confidential data is copied, transmitted, viewed, stolen or used by an individual unauthorized to do so. Data breaches may involve financial information such as credit card or bank details, personal health information, personally identifiable information, trade secrets of corporations, or intellectual property.
Researchers at Michigan State University, Ball State University, and Johns Hopkins University conducted a retrospective data analysis of data breaches reported to the U.S. Department of Health and Human Services between October 2009 and December 2016. By law, U.S. hospitals covered by the Health Insurance Portability and Accountability Act (HIPPA), must notify the HHS of any breach affecting 500 or more individuals within 60 days of the discovery of the breach.
The results revealed that during the study period, healthcare providers reported 1,225 of the 1,798 recorded breaches, while business associates, health plans, and healthcare clearinghouses reported the remaining 573 data breaches. Of these, 257 breaches were reported by 216 hospitals; importantly, 33 hospitals experienced more than one breach, many of them large, major teaching hospitals, such as UC Davis Medical Center (CA, USA) and Henry Ford Hospital (Detroit, MI, USA). The study was published on April 3, 2017, in JAMA Internal Medicine.
“This research reinforces the critical trade-off patient’s face: healthcare systems having access to information they need, versus a hacker planning to spend your savings at Best Buy,” said lead author Xuefeng Jiang, PhD, of MSU, and colleagues. “While the law requires health care professionals and systems to cross-share patient data, the more people who can access data, the less secure it is.”
A data breach is defined as a security incident in which sensitive, protected, or confidential data is copied, transmitted, viewed, stolen or used by an individual unauthorized to do so. Data breaches may involve financial information such as credit card or bank details, personal health information, personally identifiable information, trade secrets of corporations, or intellectual property.
Gold Member
STI Test
Vivalytic Sexually Transmitted Infection (STI) Array
Gold Member
SARS‑CoV‑2/Flu A/Flu B/RSV Sample-To-Answer Test
SARS‑CoV‑2/Flu A/Flu B/RSV Cartridge (CE-IVD)
Medical Examination & Procedure Light
Vega 80
Wound Irrigation Solution
Prontosan®
Latest Health IT News
- EHR Alerts Support Dosing, Sedation, and Shock Recognition in Cardiac Care
- Adaptive Radiation QA Software Gains Validation for NeoArc Treatments
- Healthcare Database Helps Close Long COVID Surveillance Gap
- Smartphone App Improves Blood Pressure Control in Hypertension
- New Tablet Platform Extends Stroke Neurorehabilitation Beyond the Clinic
- Registry-Driven Digital Outreach Boosts Use of Heart Failure Medicines
- Nurse-Coordinated Care Model Improves Heart Failure Outcomes
- Imaging Tool Quantifies Calcinosis Cutis Volume to Monitor Treatment
- Digital Symptom Monitoring Supports More Personalized Breast Cancer Care
- Short Digital Training Program Improves Motor Function in Parkinson’s Disease
- New Cloud Platform Streamlines Capsule Endoscopy Workflow and Reporting
- Smartwatch Monitoring Identifies Abnormal Vital Signs Before Routine Checks
- Weekly Remote Symptom Monitoring Improves Symptom Control in Advanced Cancer
- Digital Heart Model Supports Targeted Ablation in Atrial Fibrillation
- AI Framework Helps Clinicians Create Trustworthy Risk Prediction Tools
- AI Tool Screens for Primary Aldosteronism Using Routine EHR Data
Channels
Artificial Intelligence
view channel
AI Tool Predicts Long-Term Cardiovascular Risk from Sleep Study ECG
Sleep disorders such as insomnia and obstructive sleep apnea are established cardiovascular risk factors and are commonly evaluated with overnight polysomnography. These studies routinely record electrocardiogram... Read more
Predictive Model Supports Growth Hormone Treatment Planning in Idiopathic Short Stature
Idiopathic short stature (ISS) describes children whose height is substantially below the expected range for age and sex without an identifiable medical cause. Recombinant growth hormone therapy can support... Read more
Critical Care
view channel
Smart Tear Sensors May Help Detect Shifts in Eye Health Over Time
Dry eye disease, glaucoma, and other ocular disorders are often monitored through intermittent office visits. This approach can miss day-to-day changes in symptoms and tear-film behavior.... Read more
Wearable Smart Ring Receives FDA Clearance for Noninvasive Blood Oxygen Monitoring
Blood oxygen saturation is a key indicator of respiratory and circulatory status, and convenient tracking can support ongoing health monitoring. Wearable form factors increasingly integrate sensors that... Read more
Surgical Techniques
view channel
Vascular Occlusion System Gains Expanded FDA Indication for Venous Embolization
Venous embolization is used in peripheral veins for conditions including pelvic venous disease and portal hypertension. Physicians have faced procedure-related challenges, including the need for multiple... Read more
Tiny Robots Could Speed Targeted Drug Delivery to Heart Infections
Endocarditis is an infection of heart tissue that can become life-threatening when treatment fails to reach the infected site. About 50,000 people in the United States develop the condition each year.... Read more
Patient Care
view channel
AI Platform Personalizes Support Between Visits for Cancer Survivors
Cancer survivors often manage persistent side effects after treatment, including fatigue, anxiety, uncertainty, symptoms, stress, and questions between appointments. Clinical teams need ways to maintain... Read more
At-Home Neuromodulation Shows Promise in Selected Patients With Hypertension
High blood pressure is a major risk factor for cardiovascular disease, including heart attack and stroke. Many patients receiving treatment for hypertension still remain above recommended blood pressure... Read more
EHR Model Flags High-Risk Periods in Patients with Metastatic Breast Cancer
Determining when patients with metastatic breast cancer are nearing the end of life remains difficult, often leading to intensive interventions with limited benefit. Prognostic uncertainty can delay goals-of-care... Read more
Medical Imaging
view channel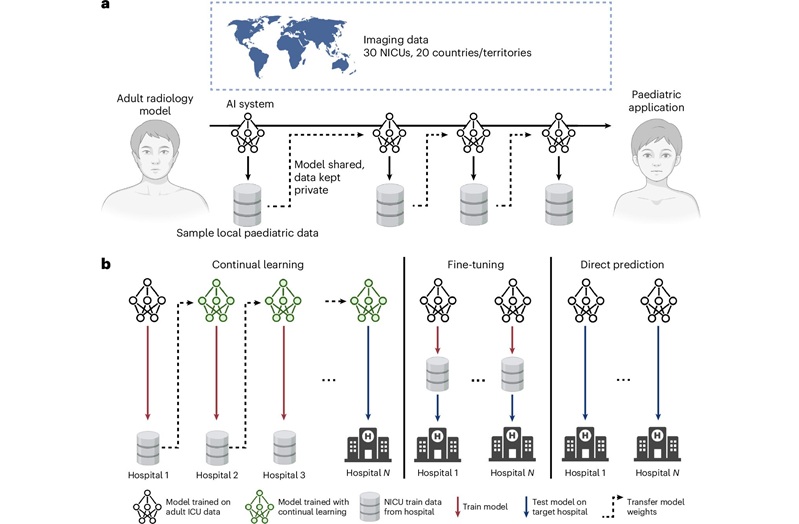
Privacy-Preserving Learning Model Adapts Adult Radiology AI for Neonatal Care
Artificial intelligence models may support radiology image interpretation, yet pediatric and neonatal care remain underserved. Privacy restrictions limit access to children’s medical records, and pediatric... Read more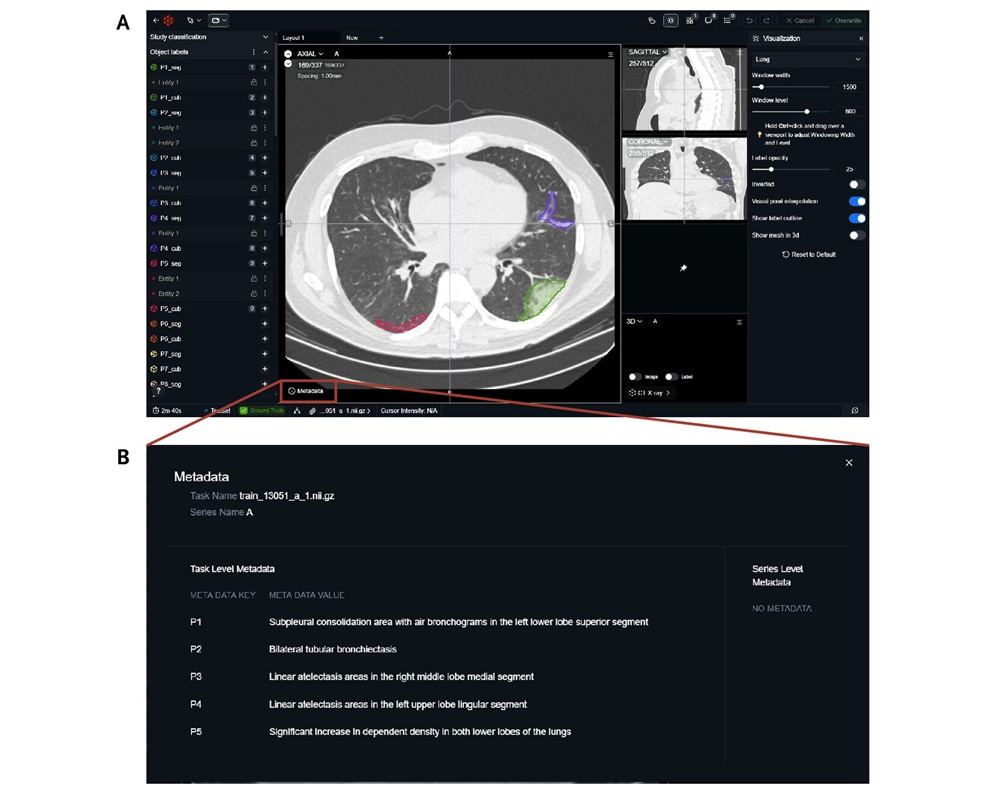
Public Chest CT Dataset Supports Explainable AI in Diagnostic Radiology
Chest computed tomography scans generate complex three-dimensional images that can be difficult for artificial intelligence systems to explain clearly. Clinicians need to verify AI findings before using... Read more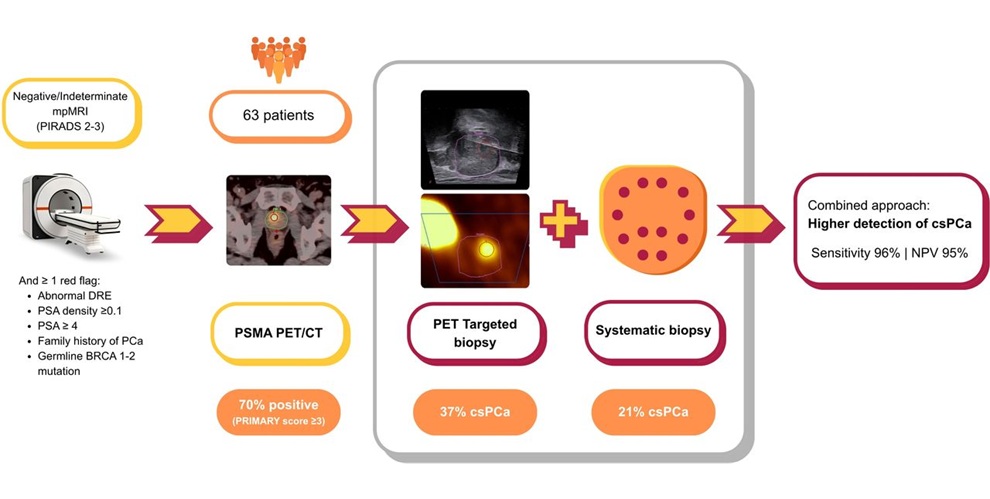
PSMA PET/CT-Guided Biopsy Improves Detection of Significant Prostate Cancer After Nondiagnostic MRI
Prostate cancer can be difficult to detect when magnetic resonance imaging (MRI) findings are negative or inconclusive. Men with persistent clinical risk factors may still require biopsy, yet standard... Read more
Point of Care
view channel
Continuous Glucose Monitoring Identifies Cardiometabolic Risk in Adults Without Diabetes
Dysglycemia—abnormal blood glucose regulation—can fluctuate throughout the day and often escape conventional screening. Clinicians typically rely on fasting plasma glucose and hemoglobin A1c, which offer... Read more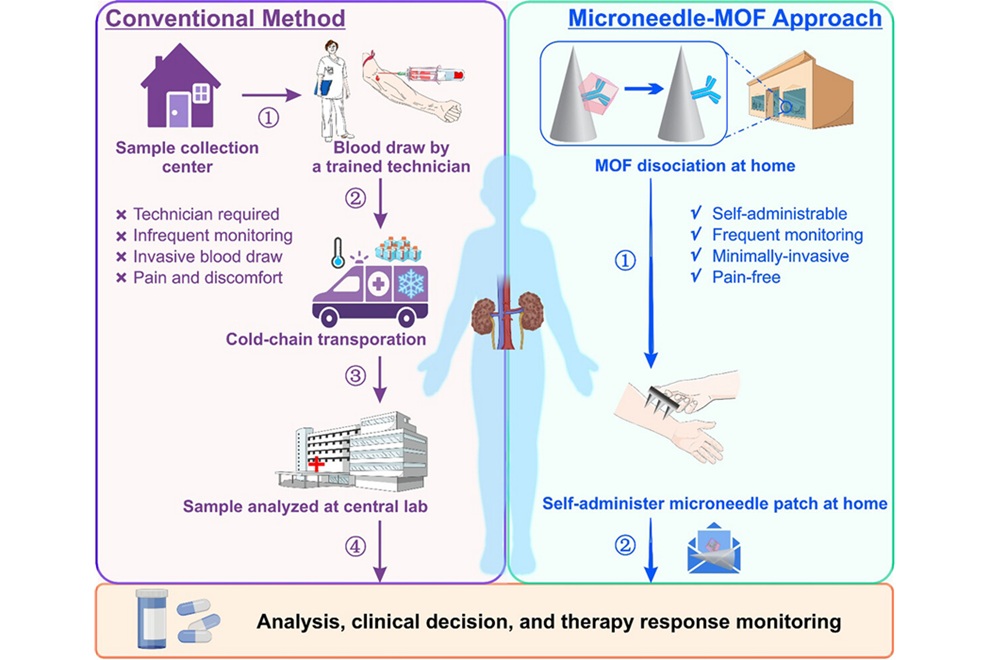
Microneedle Patch Enables At-Home Monitoring of Acute Kidney Injury
Kidney disease is often silent in its early stages, making timely detection difficult outside clinical settings. Early biomarkers such as neutrophil gelatinase–associated lipocalin can require blood draws... Read more
Business
view channel
Terumo Neuro Acquisition Advances Liquid Embolic Technology for Chronic Subdural Hematoma
Terumo Neuro (Aliso Viejo, CA, USA) signed an agreement to acquire Arsenal Medical Inc. (Waltham, MA, USA), a privately held, clinical-stage biomaterials company. The proposed acquisition would add NeoCast,... Read more
World Health Expo to Showcase Trillion-Dollar Growth Across Pharma, Biotech, Longevity and Wellness at 2027 Edition
World Health Expo (WHX) expands with the new Pharma, Biotech, Longevity and Wellness industry sectors More than 235,000 professional visits, over 4,200 exhibitors and representatives from over... Read more
Medtronic Receives FDA Clearance for Vessel-Sealing Instrument for Robotic Surgery
As robotic-assisted surgery expands across U.S. hospitals, teams increasingly seek energy instruments with the familiarity and performance of tools used in open and laparoscopic procedures.... Read more